Setup the High Side
This lab will help you setup the highside system while the oc-mirror download is working.
Recall from the architecture diagram (below) that the highside system needs to be setup to run an image registry inside the disconnected network.
OpenShift provides a mirror-registry that is purpose-built for this task.
The mirror-registry is a simplified, and portable, version of Red Hat’s Quay Image Registry.
You can use any image registry you like, as long as it supports the Docker v2 API, uses TLS encryption, and requires authenticated image pulls. Examples of alternative image registries include.
-
Harbor
-
JFrog Artifactory
-
Sonatype Nexus Repository
-
Red Hat Quay Registry (enterprise)
Lab Overview
The tasks in this lab include:
1. Transfering the installation content to the highside system using rsync
2. Connecting to the highside system and proving that it’s disconnected
3. Installing the mirror-registry
-
Trusting the generated TLS certificate
-
Logging in and creating a new pull secret
4. Uploading OpenShift’s installation images into your mirror-registry

Out-of-Order operations
In order to make good use of our time together, we will perform the tasks described above out-of-order.
We will start by copying the mirror-registry file from the jump system to the highside system, and installing it.
Installing the mirror-registry takes ~8 minutes.
We will demonstrate that the highside system is disconnected while we wait for the download to complete.
Then we will end this section by transferring the ~25GB of OpenShift installation images across the air gap and in to the disconnected mirror-registry.
Creating a Mirror Registry
Begin by using rsync to copy the mirror-registry file from the lowside system to the highside system.
We will run another rsync command a bit later to copy the installation images that oc-mirror is still downloading.
Please run the following commands in the other tmux pane that is logged in to the jump system.
rsync -avP /mnt/low-side-data/mirror-registry.tar.gz highside:/mnt/high-side-data/Warning: Permanently added 'highside' (ED25519) to the list of known hosts.
sending incremental file list
mirror-registry.tar.gz
602,655,289 100% 74.85MB/s 0:00:07 (xfr#1, to-chk=0/1)
sent 602,802,543 bytes received 35 bytes 70,917,950.35 bytes/sec
total size is 602,655,289 speedup is 1.00
Logging in to the highside system
In the real world, customers often access their disconnected systems using a VPN, a jump server, or with dedicated workstations. In your workshop environment, an exception was created in the firewall that allows the jump system to SSH to the highside system. Password-less SSH has been enabled for your convenience.
Please log in to the highside system using ssh from the jump system.
ssh highside[lab-user@jump ~]$ ssh highside Warning: Permanently added 'highside' (ED25519) to the list of known hosts. Last login: Wed Oct 8 23:29:04 2025 from 10.0.12.213 [lab-user@highside ~]$
Installing the mirror-registry
Now that you are logged into the highside system, change to the high side transfer directory (/mnt/high-side-data) and extract the mirror-registry files.
cd /mnt/high-side-data
tar -xzvf mirror-registry.tar.gz
image-archive.tar execution-environment.tar mirror-registry sqlite3.tar
The automation that installs and configures the mirror-registry takes ~5 minutes to complete.
The only option that we will provide is one to set the password for the init user to discopass.
./mirror-registry install --initPassword discopass __ __
/ \ / \ ______ _ _ __ __ __
/ /\ / /\ \ / __ \ | | | | / \ \ \ / /
/ / / / \ \ | | | | | | | | / /\ \ \ /
\ \ \ \ / / | |__| | | |__| | / ____ \ | |
\ \/ \ \/ / \_ ___/ \____/ /_/ \_\ |_|
\__/ \__/ \ \__
\___\ by Red Hat
Build, Store, and Distribute your Containers
INFO[2025-10-08 23:53:10] Install has begun
...
INFO[2025-10-08 23:57:30] Quay installed successfully, config data is stored in ~/quay-install
INFO[2025-10-08 23:57:30] Quay is available at https://ip-10-0-56-192.ap-southeast-1.compute.internal:8443 with credentials (init, discopass)
|
We can’t move on to the next step of trusting the TLS certificate until the |
Trusting the mirror-registry’s TLS certificate
The mirror-registry installer creates its own self-signed TLS certificate that is not trusted by anything, not even the highside system where it was installed.
The procedure to trust the mirror-registry’s self-signed TLS certificate is simple.
The mirror-registry install options allow users to provide their own certificate, if they were issued one, using the --sslCert option.
|
Copy the Root Certificate Authority file (rootCA.pem) that the mirror-registry created in to the Red Hat Enterprise Linux CA trust directory.
Then run the update-ca-trust command.
sudo cp -v $HOME/quay-install/quay-rootCA/rootCA.pem /etc/pki/ca-trust/source/anchors/
sudo update-ca-trust
'/home/lab-user/quay-install/quay-rootCA/rootCA.pem' -> '/etc/pki/ca-trust/source/anchors/rootCA.pem'
Log in to the mirror-registry
After the mirror-registry TLS certificate has been trusted, log in with podman.
The username is init and the password discopass.
podman login -u init -p discopass $(hostname):8443Login Succeeded!
The podman login command creates an authentication file / pull secret at $XDG_RUNTIME_DIR/containers/auth.json, for example: /run/user/1001/containers/auth.json.
|
The
|
Transfer the installation content
Make sure the oc-mirror download completed successfully before proceeding!
If oc-mirror is still downloading the OpenShift installation images, please jump forward to Prove that highside is disconnected.
But don’t forget to come back!
You can confirm the download finished by looking in your tmux pane to see if your prompt has returned, and that the .tar archive file was created.
...
2026/10/14 20:43:51  [INFO]   : === Results ===
2026/10/14 20:43:51  [INFO]   :  ✓  193 / 193 release images mirrored successfully
2026/10/14 20:43:51  [INFO]   :  ✓  5 / 5 operator images mirrored successfully
2026/10/14 20:43:51  [INFO]   :  ✓  1 / 1 additional images mirrored successfully
2026/10/14 20:43:51  [INFO]   : 📦 Preparing the tarball archive...
2026/10/14 20:50:41  [INFO]   : mirror time     : 11m6.746238255s
2026/10/14 20:50:41  [INFO]   : 👋 Goodbye, thank you for using oc-mirror
[lab-user@jump low-side-data]$
After the oc-mirror command has completed, use rsync on the jump system to copy the installation content into /mnt/high-side-data on the highside system.
|
Please run the |
rsync -avP /mnt/low-side-data/ highside:/mnt/high-side-data/sending incremental file list
./
.oc-mirror.log
186,850 100% 146.94MB/s 0:00:00 (xfr#1, to-chk=124/126)
imageset-config.yaml
469 100% 458.01kB/s 0:00:00 (xfr#2, to-chk=123/126)
mirror_000001.tar
22,931,079,168 92% 125.16MB/s 0:00:15 (xfr#2, to-chk=122/126)
... a long, but amazing, transfer ...
publish/
publish/.metadata.json
573,524 100% 655.83kB/s 0:00:00 (xfr#54, to-chk=0/112)
sent 49,601,464,493 bytes received 1,305 bytes 102,588,347.05 bytes/sec
total size is 50,192,004,929 speedup is 1.01
Prove that highside is disconnected
Looking at the workshop environment diagram, you can see how the highside system is disconnected. The highside network doesn’t provide any direct route to the internet.
|
The highside systems are configured to use a 1. The highside system allows inbound SSH & HTTP connections from the jump system 2. The highside system is allowed to install RHEL RPMs from the repos inside the Amazon AWS Cloud (not from the public repos at https://cdn.redhat.com) 3. Your disco.lab cluster will be allowed to talk to the Amazon AWS Cloud APIs. More details about this permission will be provided in the next lab 4. 🛑 Nothing else is allowed into or out of the highside network The Appendix has more information about the |
Please use the following commands to prove that the highside system is unable to connect to openshift.com and quay.io.
Recall that:
-
The
ocandopenshift-installtools were downloaded from openshift.com -
The OpenShift installation images were downloaded from quay.io
If you try to access a blocked website, like quay.io, you will see an Access Denied message like this.
curl -I quay.ioHTTP/1.1 403 Forbidden Server: squid/5.5 Date: Thu, 09 Oct 2025 00:48:08 GMT X-Squid-Error: ERR_ACCESS_DENIED 0
If you try to access an allowed website, like the Red Hat Update Infrastructure (RHUI) repos inside the Amazon AWS Cloud, you will see a message like this.
curl -I https://rhui.{aws_default_region}.aws.ce.redhat.comHTTP/1.1 200 OK Server: nginx/1.20.1 Date: Thu, 09 Oct 2025 00:48:49 GMT
If you skipped ahead to prove that the highside systems are really disconnected while the oc-mirror download was still working, it’s time to go back to Transfer the installation content.
Upload OpenShift’s installation images into the mirror-registry
Now that the highside system has: a) received the installation images, b) trusts the mirror-registry’s TLS certificate, and c) podman has logged in and created a new pull secret, you are ready to upload the installation images.
Please begin by adding the oc, oc-mirror and openshift-install commands to the PATH.
Make sure you are using the tmux pane that is logged in to the highside system.
|
sudo mv -v /mnt/high-side-data/oc /bin/
sudo mv -v /mnt/high-side-data/oc-mirror /bin/
sudo mv -v /mnt/high-side-data/openshift-install /bin/
renamed '/mnt/high-side-data/oc' -> '/bin/oc' renamed '/mnt/high-side-data/oc-mirror' -> '/bin/oc-mirror' renamed '/mnt/high-side-data/openshift-install' -> '/bin/openshift-install' [lab-user@highside ~]$
With the mirroring tools installed and configured, it is now time to run oc-mirror again, this time on the highside system, to upload the installation images in to the mirror-registry.
The upload process takes ~15 minutes in this workshop environment.
oc-mirror will create several results files in the directory where it was ran.
|
Please change directories to /mnt/high-side-data, and use the tmux pane that is logged in to the highside system to run the next command.
cd /mnt/high-side-data
oc-mirror -c imageset-config.yaml --from=file:///mnt/high-side-data/ docker://$(hostname):8443 --v2
2026/10/14 20:55:52 [INFO] :👋👋 Hello, welcome to oc-mirror 2026/10/14 20:55:52 [INFO] : ⚙️ setting up the environment for you... 2026/10/14 20:55:52 [INFO] : ⚙️ environment version: 4.20.0-202512070314.p2.gf4775a2.assembly.stream.el9-f4775a2 2026/10/14 20:55:52 [INFO] :🔀🔀 workflow mode: diskToMirror 2026/10/14 20:55:52 [INFO] : Verified we can authenticate against registry "ip-10-0-56-149.us-east-2.compute.internal:8443" 2026/10/14 20:55:52 [INFO] :📦📦 Extracting mirror archive(s)... /mnt/high-side-data/mirror_000001.tar (26.2 GiB / 26.2 GiB) [===============================================================================================================================] 7m2s 2026/10/14 21:02:55 [INFO] : 🕵 going to discover the necessary images... 2026/10/14 21:02:55 [INFO] :🔍🔍 collecting release images... 2026/10/14 21:02:55 [INFO] :🔍🔍 collecting operator images... ✓ () Collecting catalog registry.redhat.io/redhat/redhat-operator-index:v4.20 2026/10/14 21:02:55 [INFO] :🔍🔍 collecting additional images... 2026/10/14 21:02:55 [INFO] :🔍🔍 collecting helm images... 2026/10/14 21:02:55 [INFO] :🚀🚀 Start copying the images... 2026/10/14 21:02:55 [INFO] :📌📌 images to copy 199 ✓ (29s) ocp-v4.0-art-dev@sha256:0662bb5072a8076af3a038024e0a674d44938143e0a3dcc74559da39d15687a8 ➡️ ip-10-0-56-149.us-east-2.compute.internal:8443/openshift/ ... a long, mind-expanding, upload ... 199 / 199 (15m51s) [=======================================================================================================================================================================] 100 % ✓ (1m16s) redhat-operator-index:v4.20 ➡️ ip-10-0-56-149.us-east-2.compute.internal:8443/redhat/ 2026/10/14 21:18:46 [INFO] : === Results === 2026/10/14 21:18:46 [INFO] : ✓ 193 / 193 release images mirrored successfully 2026/10/14 21:18:46 [INFO] : ✓ 5 / 5 operator images mirrored successfully 2026/10/14 21:18:46 [INFO] : ✓ 1 / 1 additional images mirrored successfully 2026/10/14 21:18:46 [INFO] : 📄 Generating IDMS file... 2026/10/14 21:18:46 [INFO] : /mnt/high-side-data/working-dir/cluster-resources/idms-oc-mirror.yaml file created 2026/10/14 21:18:46 [INFO] : 📄 Generating ITMS file... 2026/10/14 21:18:46 [INFO] : /mnt/high-side-data/working-dir/cluster-resources/itms-oc-mirror.yaml file created 2026/10/14 21:18:46 [INFO] : 📄 Generating CatalogSource file... 2026/10/14 21:18:46 [INFO] : /mnt/high-side-data/working-dir/cluster-resources/cs-redhat-operator-index-v4-20.yaml file created 2026/10/14 21:18:46 [INFO] : 📄 Generating ClusterCatalog file... 2026/10/14 21:18:46 [INFO] : /mnt/high-side-data/working-dir/cluster-resources/cc-redhat-operator-index-v4-20.yaml file created 2026/10/14 21:18:46 [INFO] : 📄 Generating Signature Configmap... 2026/10/14 21:18:46 [INFO] : /mnt/high-side-data/working-dir/cluster-resources/signature-configmap.json file created 2026/10/14 21:18:46 [INFO] : /mnt/high-side-data/working-dir/cluster-resources/signature-configmap.yaml file created 2026/10/14 21:18:46 [INFO] : mirror time : 22m54.166459262s 2026/10/14 21:18:46 [INFO] : 👋 Goodbye, thank you for using oc-mirror [lab-user@highside high-side-data]$
|
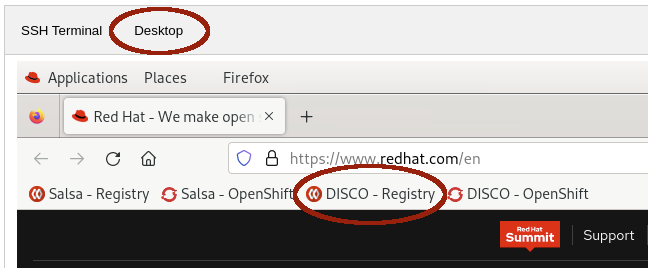
You can click the Desktop button and use Firefox to login to your new Reminder: The credentials for your DISCO - Registry are: |
|
As a convenience, the jump system has been configured to automatically trust the highside mirror-registry’s TLS certificate. This automation means workshop participants don’t have to:
You’re welcome! |